Binarly said on Nov. 3 that the exploit used against Zyxel GS1900 switches still works on all ten June fix releases, so a ticket closed on that patch does not mean the switch is safe. Owners should treat those switches as exposed, isolate the management interface and check for compromise before updating to the October firmware.
Why Binarly says the June fix did not hold
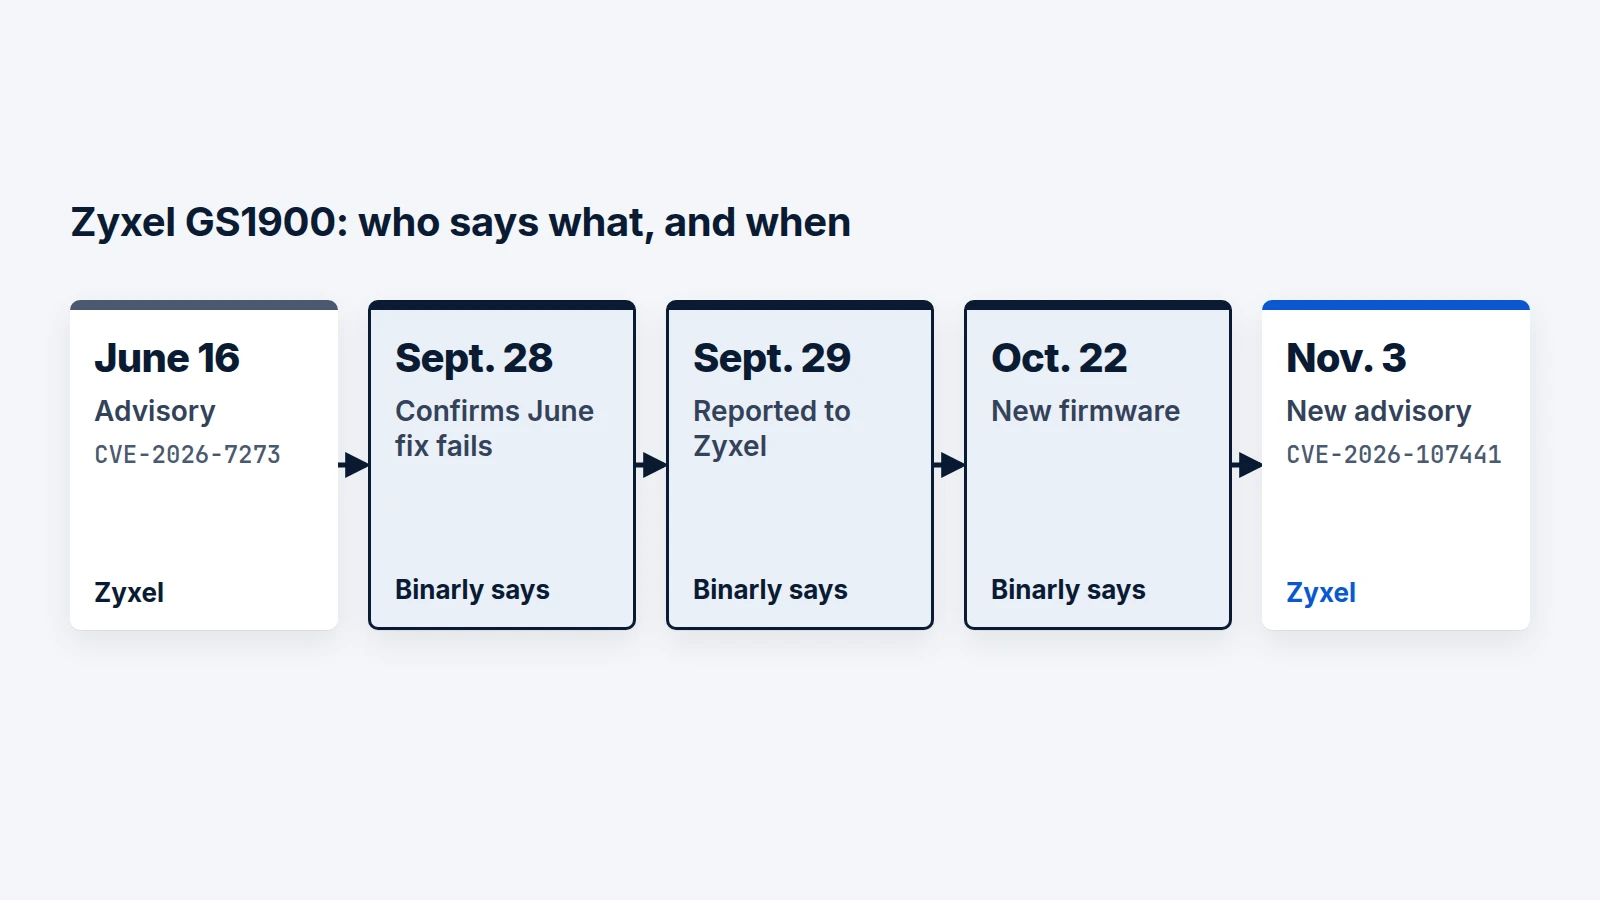
Binarly's research post says it confirmed on Sept. 28 that all ten releases remain vulnerable to the exploit, which works without changes. In its account the fix checked a counter only after it was corrupted.
Zyxel's June 16 advisory covered CVE-2026-7273. GreyNoise wrote on Sept. 21 that on or about Aug. 17 an actor took configurations, hashed root-level credentials and networking information from 996 GS1900 switches in 48 countries. GreyNoise tied that to CVE-2026-7273; CISA added the CVE to KEV on Sept. 21.
Binarly's advisory says it told Zyxel on Sept. 29, and dates Zyxel's confirmation to Oct. 11 and the fixed firmware to Oct. 22. Zyxel published no advisory until Nov. 3. That advisory, for CVE-2026-107441, says a LAN-based, unauthenticated attacker could potentially execute OS commands via a crafted HTTP request, and makes no statement on exploitation. Binarly wrote that Zyxel treats its report as a separate vulnerability. Binarly scores the flaw 9.8, network attack vector, because an attacker only needs reachability to the management service; Zyxel's CVE record says 8.8, adjacent.
Was the new flaw exploited?
Whether CVE-2026-107441 was exploited rests on Binarly alone. Its post calls it a zero-day; its advisory allows two readings: Zyxel's June patch was wrong, or CISA's link between the GreyNoise activity and CVE-2026-7273 was wrong. Either way, it wrote, all ten fix releases are vulnerable. The KEV feed released Nov. 4 does not list CVE-2026-107441. CISA's enrichment on the CVE record showed exploitation "none" on Nov. 4.
Who is affected, and were patched switches hit?
Owners of GS1900 switches on the June releases or earlier firmware. No source says which firmware GreyNoise's 996 victims ran, so it is unknown whether June-patched switches were among them. The 996, 129 of them in the US, are not a count of exposed devices; 564 had factory default credentials. Zyxel patched only models within its support period; it calls unlisted on-market products unaffected and does not address off-market ones.
What to do now
- Network team, today: find every GS1900 and check from outside whether its management interface answers. Put it on a management network and block switch-initiated outbound traffic except to the syslog, RADIUS, NTP and SNMP servers you run.
- Admins, today, once the interface is isolated: replace default credentials. In our view, if an interface was ever reachable from an untrusted network since Aug. 17, assume the configuration was copied and rotate the admin password, SNMP strings and RADIUS secrets.
- Security team, this week, before the update: save logs and a config backup. Patching can destroy evidence, so CISA's guidance tells federal agencies to collect it first; we suggest copying that. Search egress for traffic from switch management addresses to GreyNoise's published indicators, and for outbound TFTP to a server you do not run, notably UDP destination port 6969. If you have shell access, look for
/home/web/tmp/info.txt. This check is partial. No source says whether the file survives a reboot, so its absence proves nothing. On any match, we advise reflashing rather than trusting a version check, and reviewing what the switch could see. - Network team, this week, once evidence is saved: install the firmware Zyxel released for CVE-2026-107441. Zyxel's table lists each model (GS1900-24: 2.90(AAHL.3)C0). Binarly plans to publish a minimized proof of concept "in the near future".
- Owners of off-market GS1900 models not in Zyxel's table, this quarter: plan replacement; Zyxel lists no fix.