Practical defense
against AI-era attacks
Attackers are using AI to move faster. We break down real incidents, show how to defend with AI agents, and lay out the data-handling procedures that stop a breach from spreading.
Latest incidents and guides
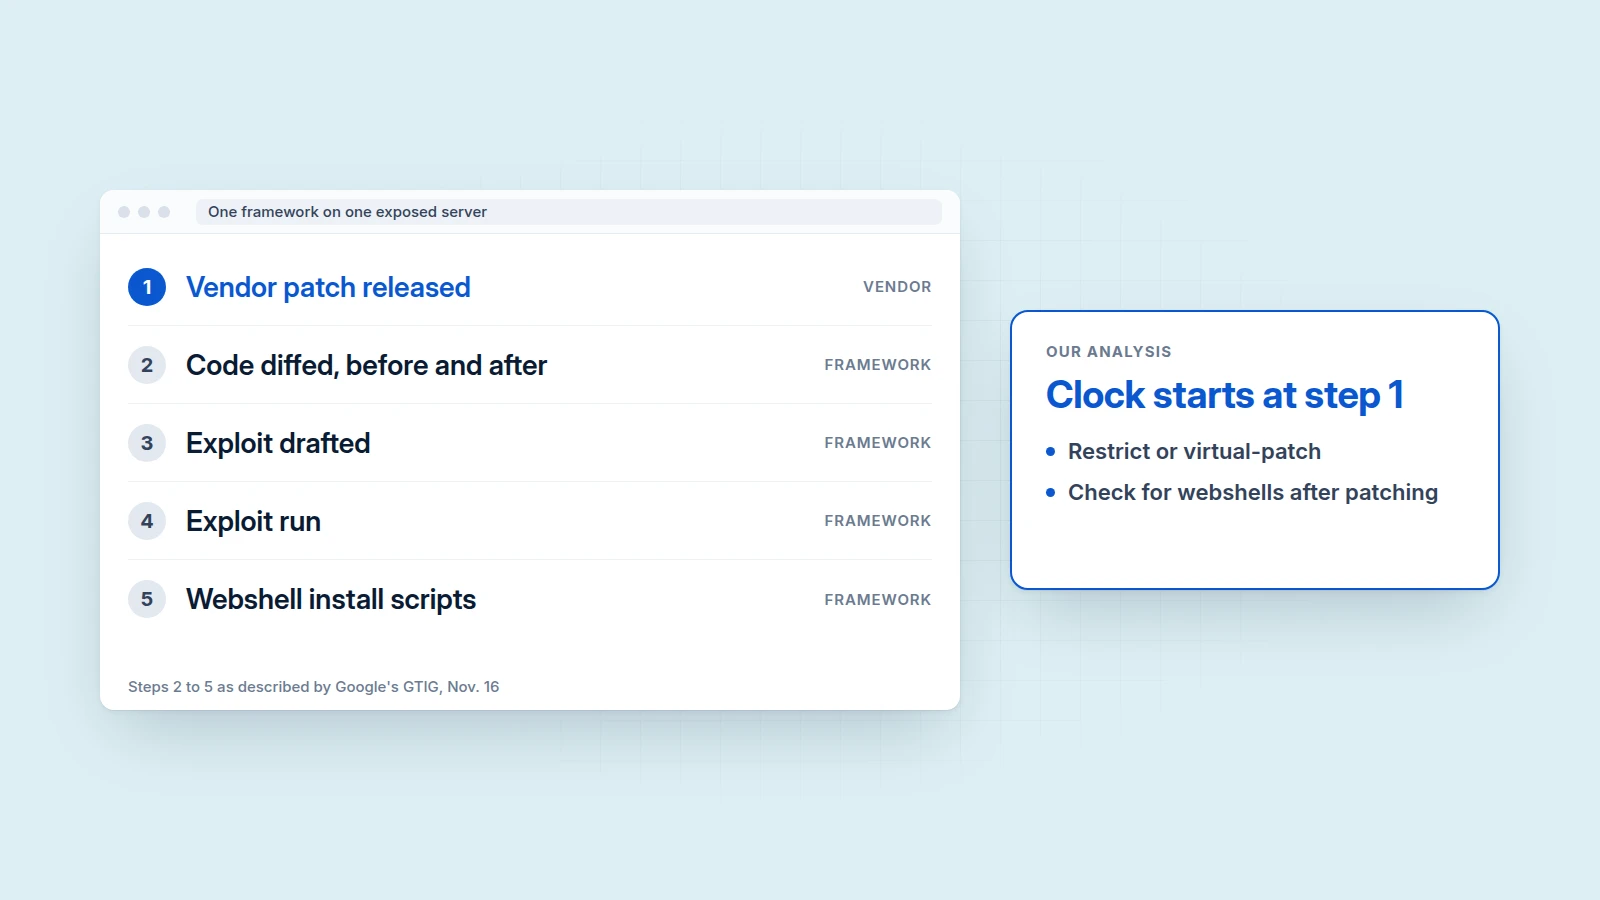
Google says one attacker framework diffs web-app patches and runs the exploits without a human
Google's threat intelligence group describes a framework on one exposed server that turns patches into exploits. We would start the emergency patch clock at the vendor's release, not at a KEV listing.
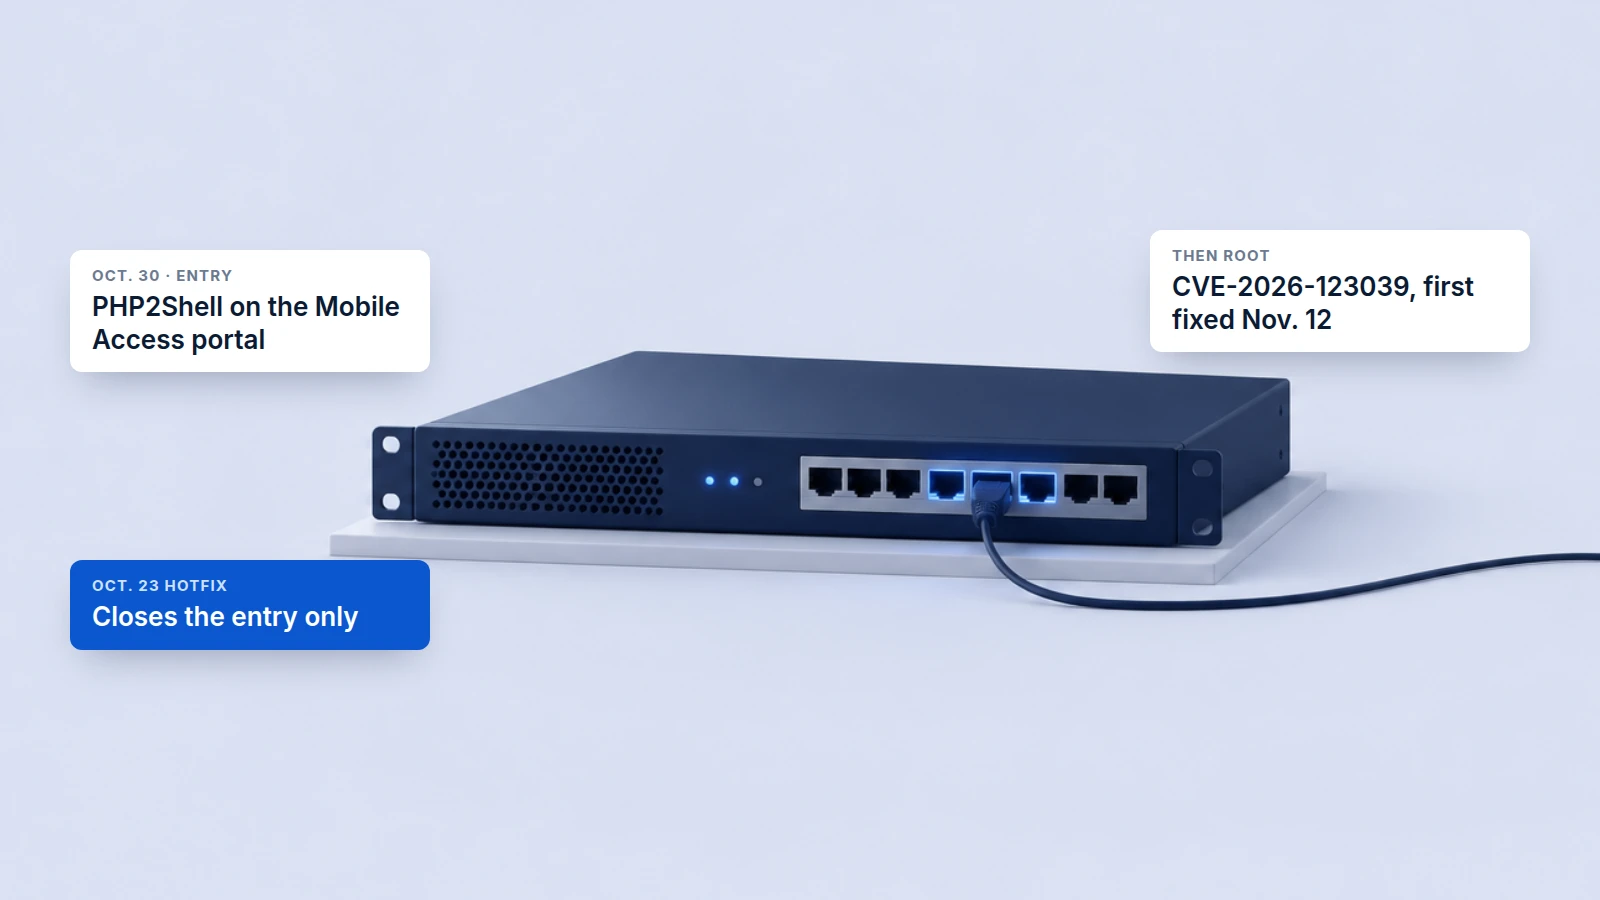
Check Point says attackers chained PHP2Shell with a root flaw it first fixed on Nov. 12
Attackers entered unpatched Check Point Mobile Access portals through PHP2Shell, then took root. The October hotfix closes only the entry; the November Jumbo takes close both where Check Point has released them.
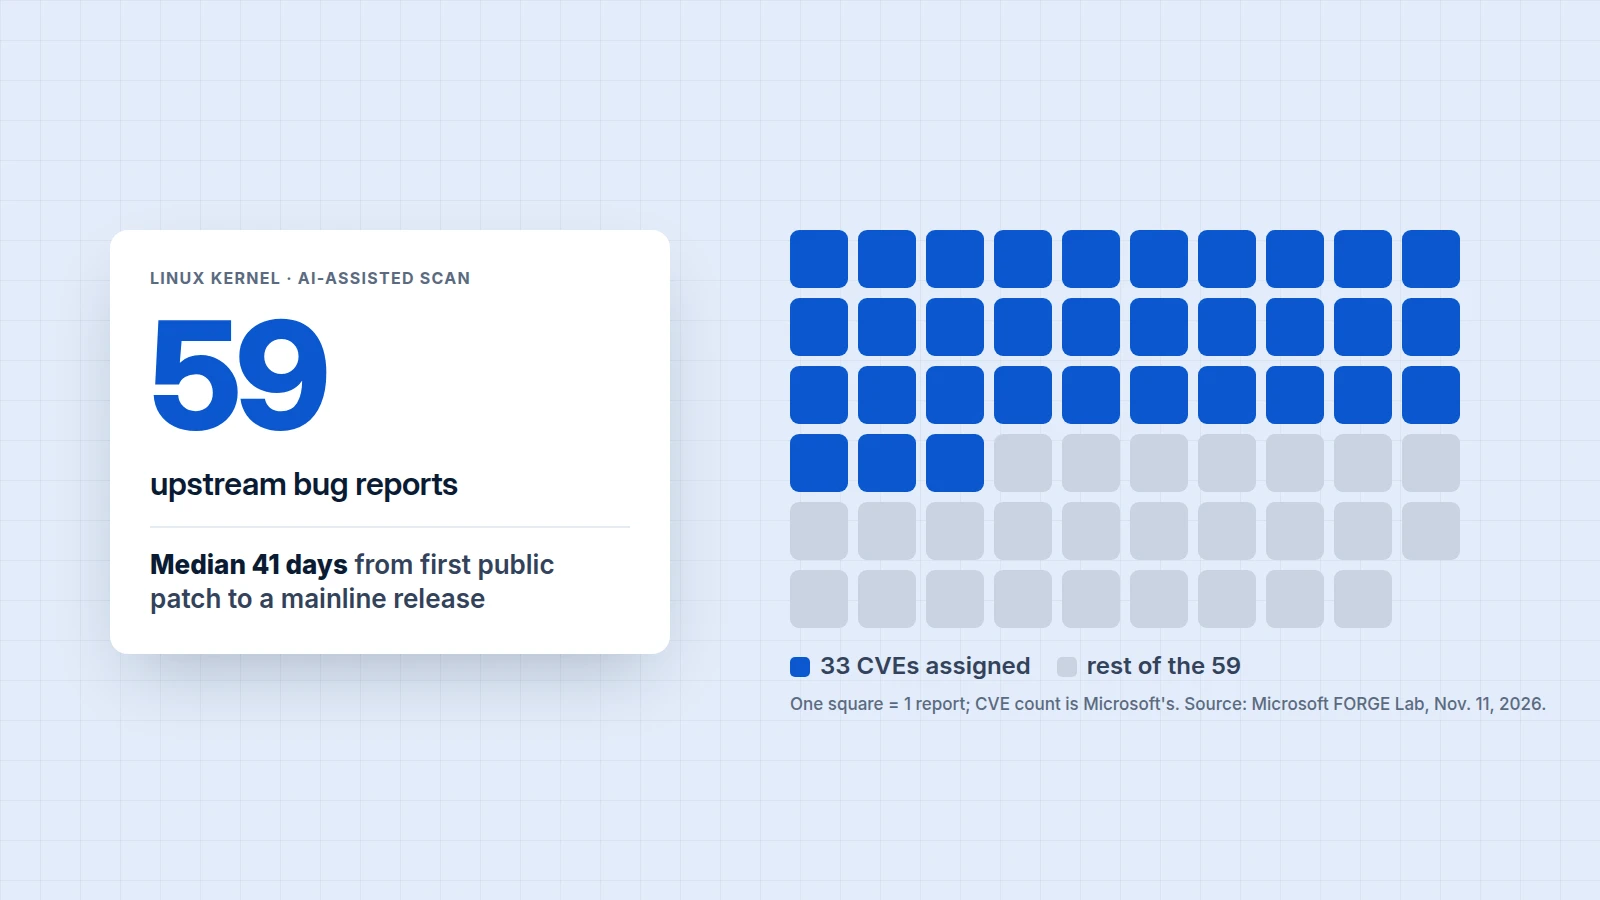
Microsoft's AI-assisted scan found Linux kernel bugs averaging 8.1 years old, so track the running kernel
Microsoft says its FORGE Lab scan produced 59 upstream reports and 33 CVEs. One lab root exploit needs no user namespaces, so patching and detection matter as much as disabling modules.
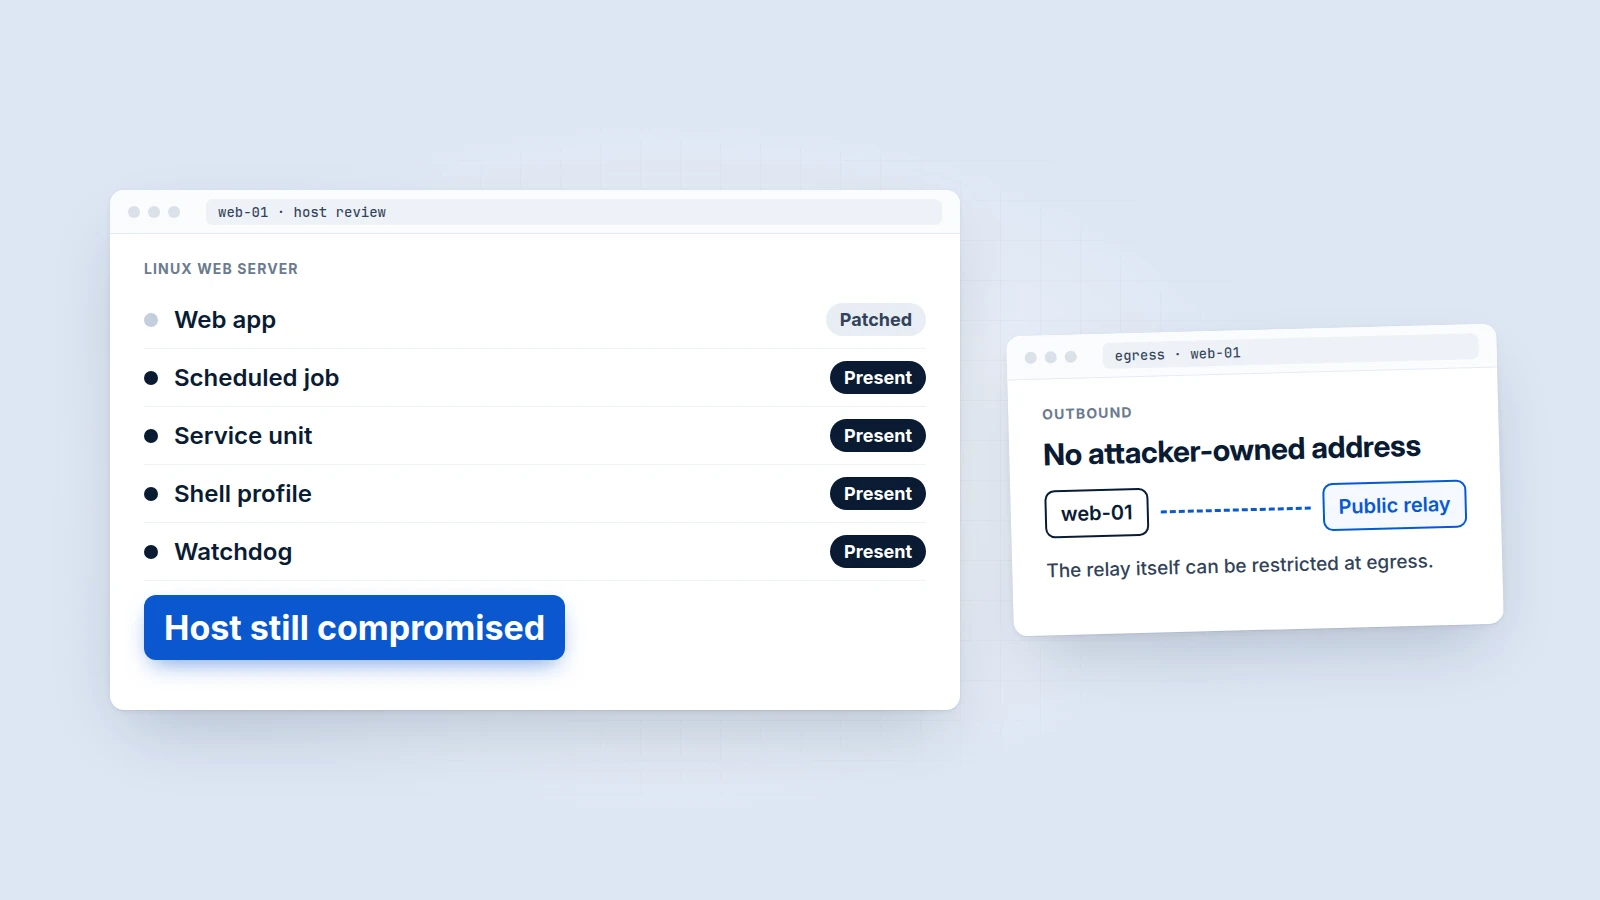
Microsoft: patching the web app does not remove GSocket planted on Linux web servers
Unrelated threat actors deployed GSocket after exploiting web apps and kept access after the flaws were remediated, Microsoft said Nov. 11. Our read: the host needs its own hunt.
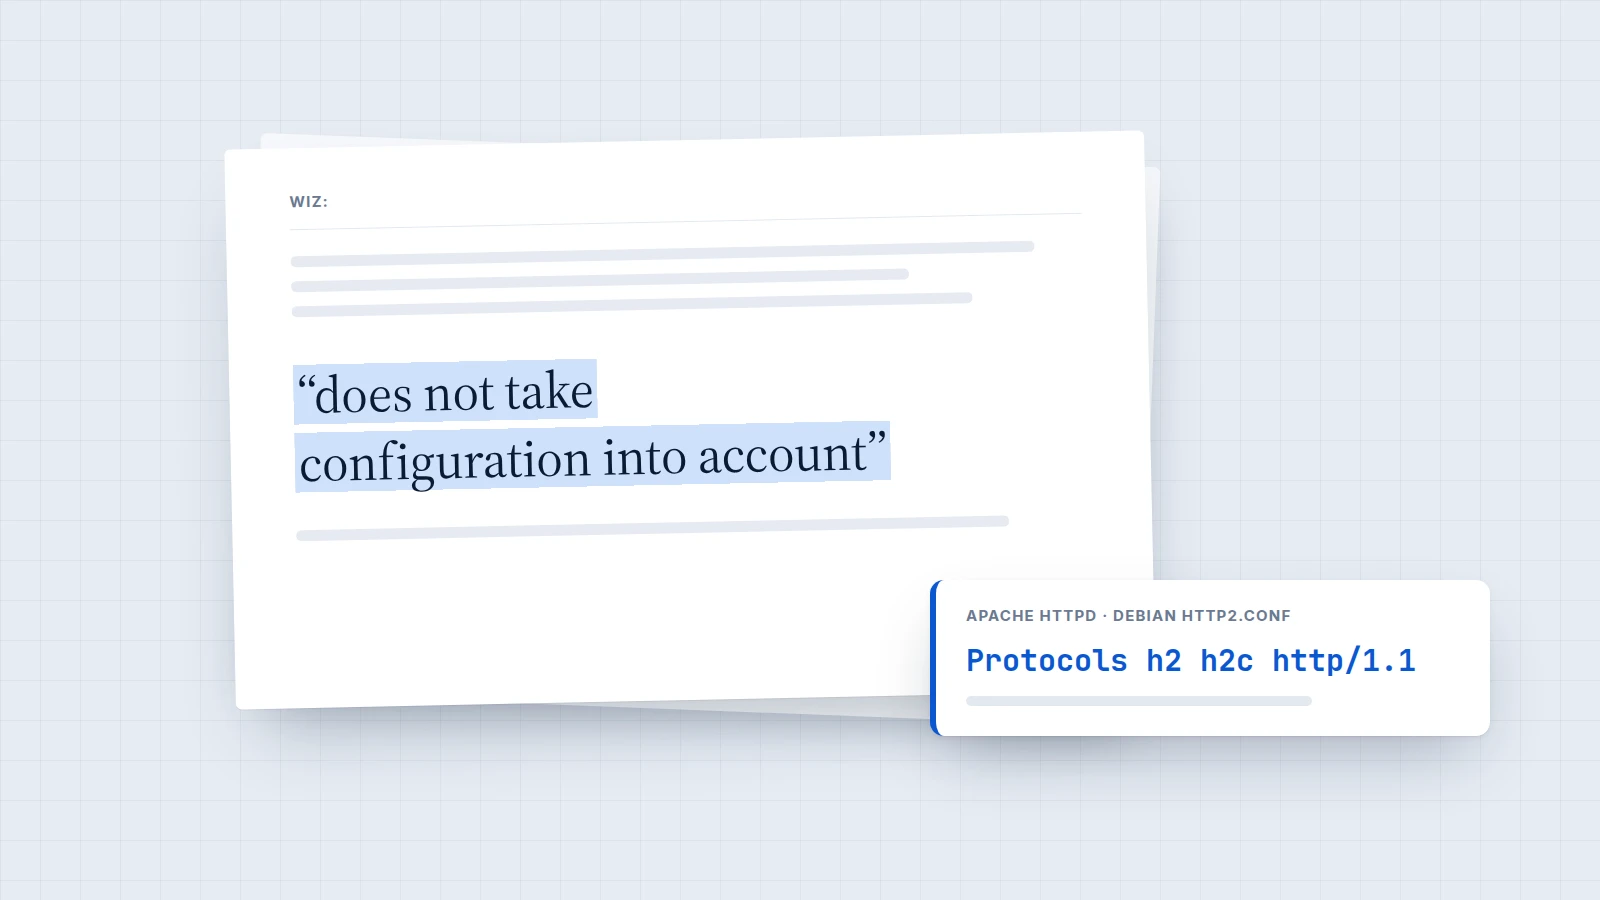
Apache's critical mod_http2 flaw reaches only servers that speak HTTP/2: check each host, then patch or turn h2 off
CVE-2026-119618 affects Apache httpd 2.4.55 through 2.4.70, but only hosts with HTTP/2 enabled are reachable. Find them, patch internet-facing ones first, and know what the workaround breaks.
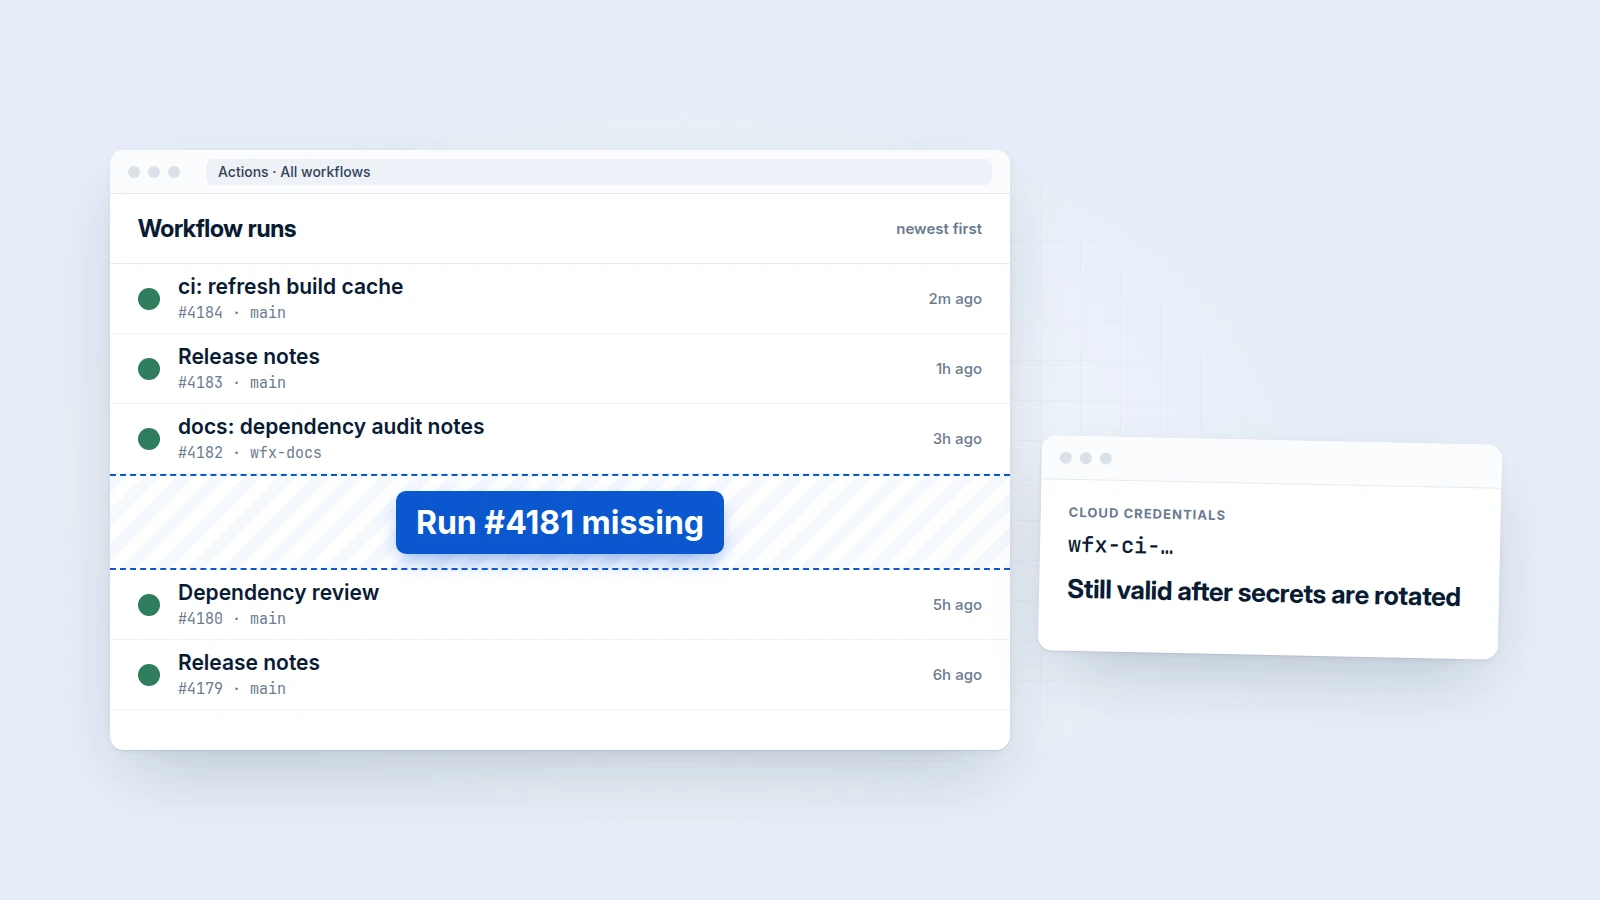
Hijacked GitHub accounts ran a CI secret stealer and deleted the run, so a missing run number is the trace
Aikido says stolen credentials let attackers run a stealer in at least 1,800 repositories from Nov. 10. The actor reverted within a minute and deleted the runs and logs.
Browse by topic
Guides and checklists
Procedures, checklists and fill-in plans for handling data and running an incident.
All guides- Business Email Compromise Response: The First 24 HoursHow-to
- Data Breach Notification Laws by State: Which Deadline BindsHow-to
- HIPAA breach notification: from the discovery date to the HHS reportHow-to
- Ransomware Response Playbook: Decisions for the First 72 HoursHow-to
- New York data breach notification law: residents within thirty days, three state agencies and, for DFS licensees, a DFS report within 72 hoursOverview
- California data breach notification law: notice to residents within 30 calendar days, the Attorney General copy and what triggers themOverview
Defense first
We explain how an attack works so you can stop it. We do not publish working exploits.
Facts checked against their sources
Claims are checked against their sources before publication. Versions, prices and other values that change are re-checked afterward.
Responsible disclosure
Found a flaw in something we cover? Write to the editors at contact@cybersecurity.guru.