Facts checked Nov 5, 2026
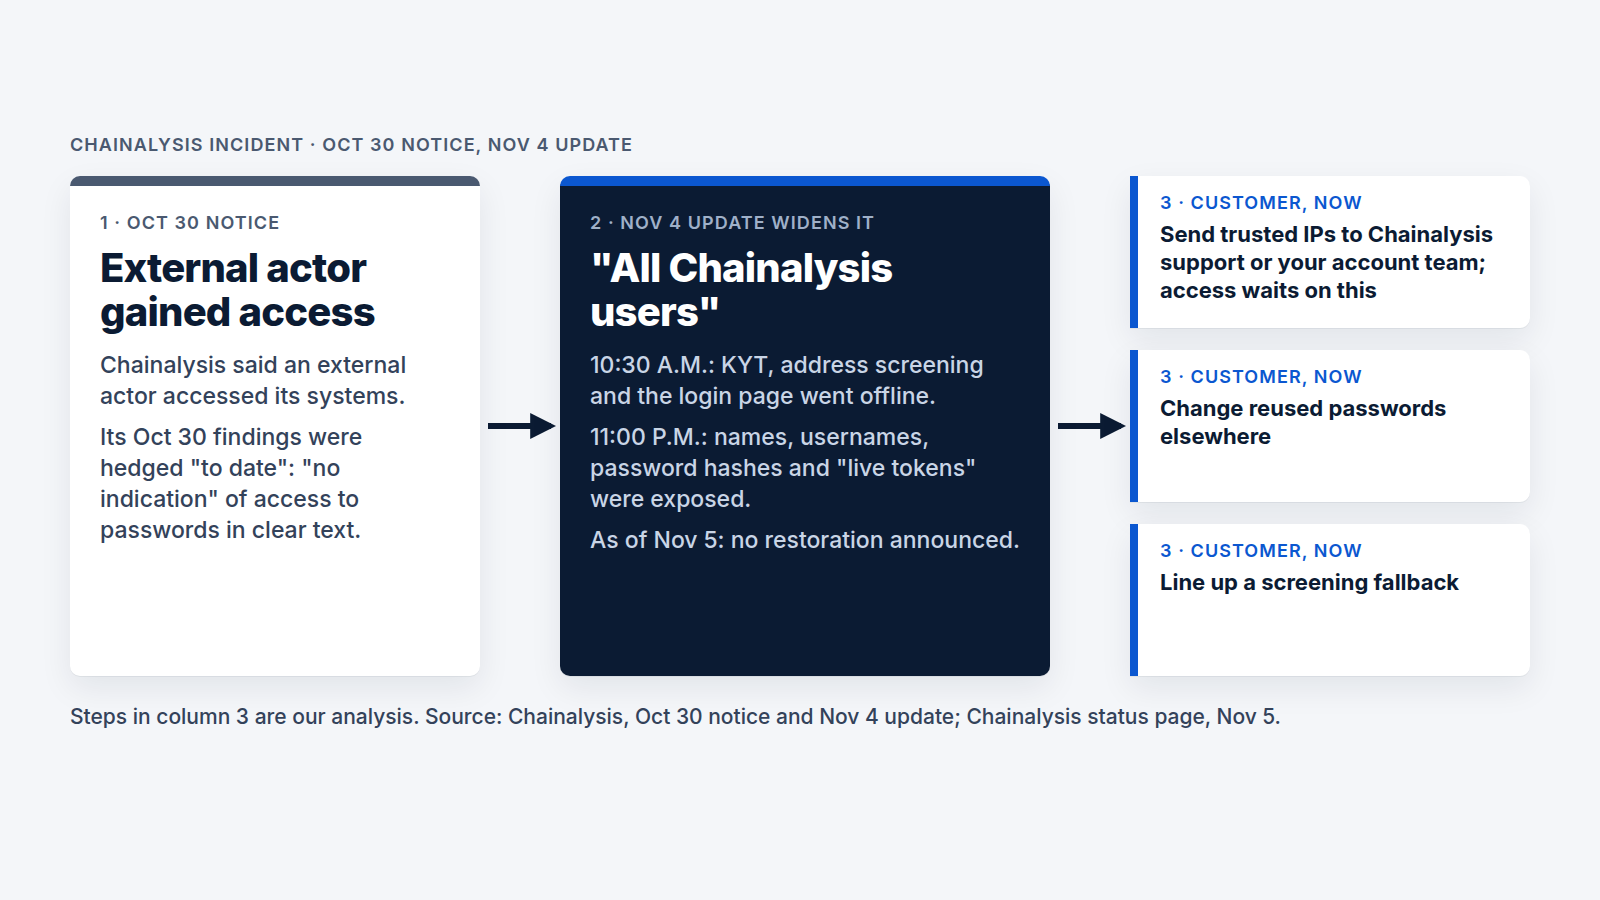
Chainalysis said on Nov. 4 that names, usernames, password hashes and "live tokens" for "all Chainalysis users" were exposed. Treat every provisioned user's Chainalysis password and token as compromised, and act now on what needs no login: reused passwords, trusted IPs, a key-rotation owner, a screening fallback.
What Chainalysis said
On Oct. 30 Chainalysis said an external actor using "offensive agentic techniques" gained access to its systems, with, to date, "no indication" of access to passwords in clear text, MFA secrets or user session tokens, and "no evidence" on "authentication credentials."
Nov. 4 widened that:
- 9:50 A.M. EST: an email to "certain customers whose Chainalysis passwords were exposed in an 'on-path attack,'" which it called "contained and remediated." The email cited an "ongoing multifront cyberattack."
- 10:30 A.M.: because of "abnormal activity," KYT, address screening products and the login page went offline. Resetting "won't be possible right now."
- 11:00 P.M.: "On Monday, we discovered certain customer information including names, usernames, password hashes and live tokens for all Chainalysis users were exposed to a malicious actor." "Monday" means Nov. 2. It says "exposed," not stolen or cracked, and has not defined "live tokens" or said whether they were revoked. It still has "no evidence" that investigations data was accessed or attribution data manipulated. It does not address MFA secrets or query results. It is notifying "customers whose KYT accounts appear to have been accessed without authorization," with no count.
As of Nov. 5, Chainalysis has not said whether the on-path passwords and the hashes are one event.
Chainalysis wrote "We intend to begin restoring access to KYT and Address Screening tomorrow" (Nov. 5) and that every user must "reset passwords and rotate API keys as appropriate." Send trusted IPs first to support@chainalysis.com or your account team; it will "then grant access." The status page's last update, 20:38 UTC Nov. 5, announced no restoration; components showed KYT API and UI, Address Screening, Reactor, Investigations API, Rapid Lookup and Sentinel as under maintenance. The blog also names Data Solutions, with no date for it or Reactor.
Hexagate: on Nov. 4 at 17:35 UTC the status page said customer API keys were invalidated, with "no evidence that API keys were exposed," and login working through app.hexagate.com. As of Nov. 5, no source says this of KYT or Reactor keys.
Who is affected
Chainalysis says "all Chainalysis users," though The Record noted the statement does not say every category applies to every user. As of Nov. 5, it gives no user or US count.
What to do now
- KYT API owner, today: list every integration using a Chainalysis API key, name who rotates it and how it deploys. Hexagate customers: rotate in the Hexagate UI.
- Vendor-account owner, today: send trusted IPs. Access waits on this.
- Identity team, today: have every provisioned user change reused passwords elsewhere, as Chainalysis advised emailed customers. Warn them that reset emails may be lures; per Chainalysis, skip their links and use the login page directly once it returns.
- Compliance lead, today: extend your Reactor fallback to KYT and address screening, including transactions unregistered during the outage. Expect staged restoration.
- SOC, within 24 hours: pull SSO sign-ins to Chainalysis and your KYT API call logs; ask for tenant activity logs. No notice is not an all-clear.
Vendor-account owner: ask Chainalysis in writing what "as appropriate" and "live tokens" cover, whether they were revoked, the hash algorithm, when exposure began, whether its MFA-secrets finding still holds, and which "additional protections" it will require for access.