DigiCert customer notices seen publicly by Nov 4 list business contact data and possibly ID documents. DigiCert reports no certificates affected, so leave certificates alone and warn the staff named as contacts or who submitted documents about phishing.
What happened
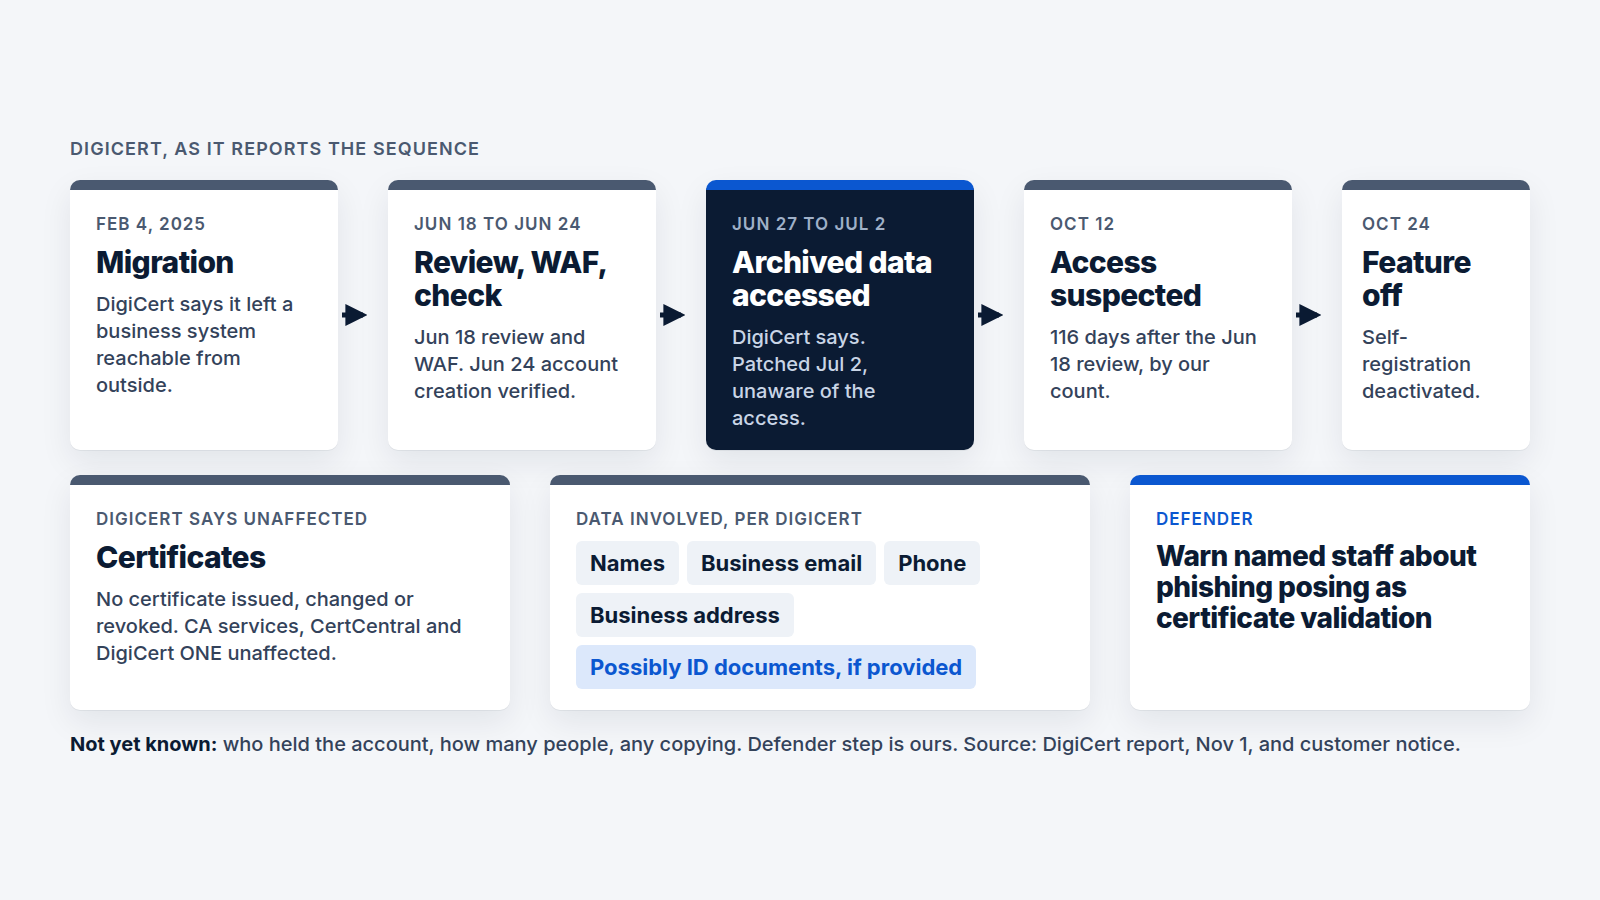
In its incident report on Bugzilla, posted Nov 1, DigiCert said a migration on Feb 4, 2025 left an internal business system reachable from outside. A registration feature meant for other uses became available on it. Accounts registered there skipped MFA and defaulted to read-only, yet could read archived data. DigiCert said an account accessed archived data from Jun 27, 2026 through Jul 2.
The notice, posted by Troy Hunt on Nov 4 and more fully by another recipient, says the information was limited to names, business email addresses, phone numbers and business addresses and, "if provided, may have included an identification document" such as a driver's license, passport or utility bill. DigiCert says it is "completing a review" to find the individuals involved and will notify them. It also says it is the data controller, is "handling all individual and regulatory notices" and that "Your organization will not be mentioned in any regulatory filing." In our view that does not settle what a customer owes its own staff.
DigiCert said the access could not write records, approve validations or issue certificates, and that no certificates were issued, modified or revoked. It said CA services, CertCentral and DigiCert ONE were "unaffected" and customer login credentials remain secure.
What the timeline shows
By our count, the Jun 18 review, which found non-DigiCert accounts and concluded they had no data access because none was assigned to an application, came nine days before access first occurred and 116 days before DigiCert first suspected data access, on Oct 12. DigiCert wrote that "initial reviews concluded incorrectly," which delayed detection. The system moved behind a WAF on Jun 18, and DigiCert verified the account-creation ability on Jun 24, three days before access began. The Jul 2 patch blocked registration and unassigned accounts' reads, with DigiCert unaware of the access; the self-registration feature was deactivated Oct 24. Our analysis: on DigiCert's dates, a Jun 18 read-history check would have found nothing; the test that mattered was what the accounts could reach.
Who is affected
Those affected are customer representatives whose details are in the data. DigiCert says a "small proportion" of archived data was involved, and a "small minority" of customer accounts included a personal document.
What to do now
- PKI lead, today: leave certificates alone. DigiCert says no action is needed on active ones.
- PKI lead and IT, this week: list everyone who submitted validation documents or is named as a contact. Ask your DigiCert contact whether they are in scope; its review is still running, so do not wait.
- Security awareness, this week: warn them about phishing posing as certificate validation or renewal, and have them confirm such requests through a known channel.
- Privacy or legal, this week: ask counsel whether you owe those staff anything, given DigiCert's position. At the next vendor review, add CA validation records to your vendor data list.
- Platform owners, this quarter: treat a network accessibility change as a security change. When an unexpected account turns up, test what an identical account can reach, disable the original, then re-check its activity after the fix. DigiCert's lesson: authorization must not rest on network position.
What is not known yet
As of Nov 5, DigiCert's report names no one who held the account. It does not say how many people are affected, which documents were involved or whether anything was copied.