Facts checked Nov 12, 2026
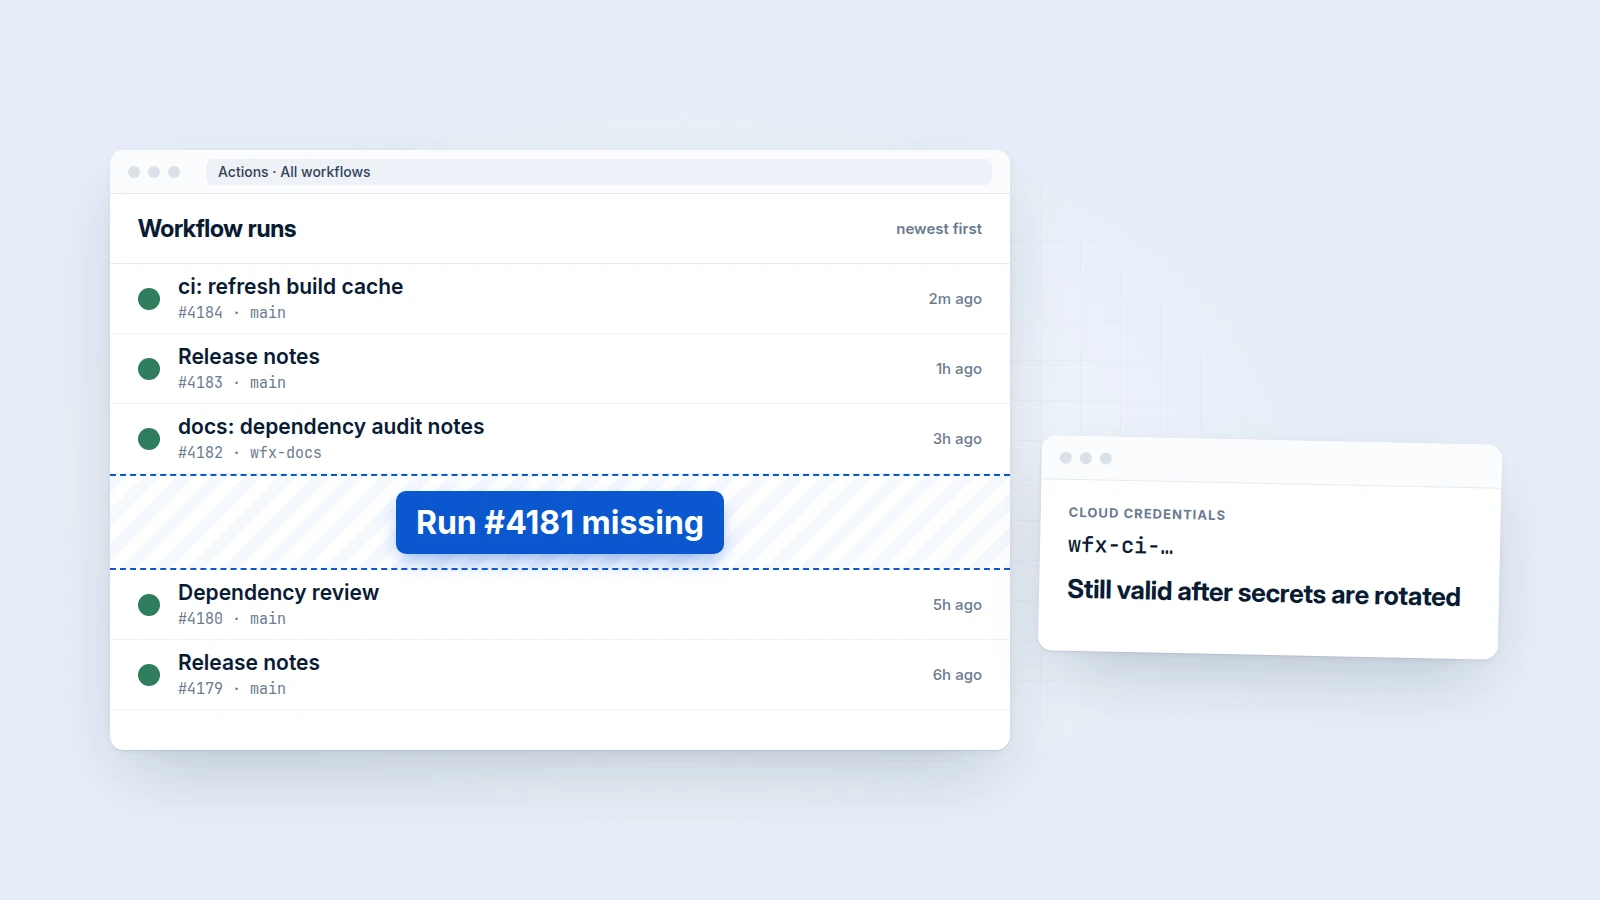
Aikido Security says hijacked GitHub accounts ran a CI secret stealer in at least 1,800 repositories from Nov. 10, then deleted the runs and logs, so the usual check shows nothing. Look instead for a missing run number and the probe pull request, and treat any repository where it ran as having leaked every secret and cloud role, including access that survives rotation.
What happened
Aikido Security reported on Nov. 12 that accounts with stolen GitHub credentials opened pull requests titled "docs: dependency audit notes" from a branch named wfx-docs to confirm write access. Where that worked, the payload arrived one of three ways: a step injected into an existing workflow, a postinstall hook that runs a .ci-.sh script, or a throwaway branch with a build-audit-.yml workflow. Commits were titled like "ci: refresh build cache" or "chore: add ci helper".
Aikido wrote that the actor reverts within at most one minute and deletes the workflow run with its logs, and that a missing run number "is often the only trace."
The payload went after Actions secrets and variables, runtime tokens, cloud and developer credential files, AI provider keys and, on self-hosted runners, instance metadata credentials. It also minted OIDC tokens and exchanged them for AWS, GCP and Azure access. Aikido saw HTTP POST to two IPs. SafeDep also saw a third IP and Telegram; about a fifth of its 200-commit sample used Telegram only.
Aikido says that in the clouds the payload creates IAM access keys, rewrites an AWS role trust policy so the role is open to any AWS account, and adds Azure federated credentials named wfx-ci-..., which keep working after every token is rotated. Aikido reports it can also post forged "success" status checks; SafeDep found that code but no sample that turned it on.
Who is affected
By Aikido's count, 4,837 accounts opened probe PRs in 61,764 repositories, and the payload ran in at least 1,800 (the post gives 1,835 and 1,806 in different places and may understate). Of the PRs, 10,431 went into repositories the account does not own, reached through collaborator or organization access. SafeDep counted 8,093 repositories with malicious commits, a different measure.
Packages Aikido names: Packagist digitalelvis/neuronai-studio 3.14.3 (treat machines that installed it as compromised) and Go github.com/onuragtas/docker-env v1.0.278 and v1.0.280 (payload in a workflow file only). SafeDep also lists docker-env v1.0.282 and the Go pseudo-version github.com/vkuznet/gocurl v0.0.0-20261111095532-8d5aad0cb0da.
What to do now
- Security engineering, today: search your organizations and every repository your people can write to for the PR title, the branches wfx-docs, chore/ plus eight characters and ci-check- plus four digits, and those commit messages. Check workflow history for gaps in run numbers from Nov. 10; Aikido's search starts there, so go back further if your history allows.
- Identity team, today: if a PR came from a developer account, revoke that user's tokens, OAuth grants, SSH keys and sessions. Where the payload ran, rotate every secret and revoke every cloud role its workflows could reach.
- Cloud team, today: in CloudTrail, find AssumeRole or AssumeRoleWithWebIdentity with session names starting wfx-, then CreateAccessKey or UpdateAssumeRolePolicy. Review trust policies for any-account principals and new IAM keys, Entra app registrations for wfx-ci- credentials, and GCP service account token generation.
- Repo admins, this week: review branch protection history for status checks posted by something other than your CI.
- Network team, today: block 194.150.166[.]244, 18.143.168[.]96 and 153.75.82[.]159 (port 8080; /exfil on the first two). Stealer SHA-256: 89695abb392d5cfd4972672961e644bb46baa98aa1ed7173c2a2816c762735cf.
- Platform team, this quarter: we recommend narrowing OIDC subject conditions and requiring fine-grained or SSO-bound tokens.
What is not known yet
Neither source says how the credentials were stolen. Aikido links some accounts to October's GhostActions wave but assesses the campaigns as distinct, likely by different actors.